AWS Cloud Security Assessment in Saudi Arabia
Review AWS security controls, relevant configurations, access patterns, and potential exposure to identify weaknesses that require investigation or remediation.
SecureLink provides AWS security consulting in Saudi Arabia for organizations that need to assess cloud security risks, review configurations, strengthen identity and access controls, and improve compliance readiness. We evaluate AWS security controls against the organization's infrastructure, workload requirements, access policies, and operational responsibilities.
Our AWS security consulting services help identify configuration weaknesses, excessive permissions, security gaps, and control deficiencies that may expose cloud workloads to unnecessary risk. Recommendations are prioritized according to risk, business impact, and practical remediation requirements.
This page focuses on AWS security assessments, cloud security configuration, IAM reviews, and compliance consulting. Broader cloud architecture, migration, managed operations, landing zones, and Well-Architected reviews are covered on their dedicated service pages.
Evaluate AWS security controls, configurations, and potential exposure across your cloud environment.
Review identity permissions, access policies, roles, and privilege assignments to identify excessive or inappropriate access.
Examine relevant AWS service configurations and security settings to identify weaknesses and improvement opportunities.
Map relevant security requirements to AWS controls, supporting evidence, and remediation priorities.
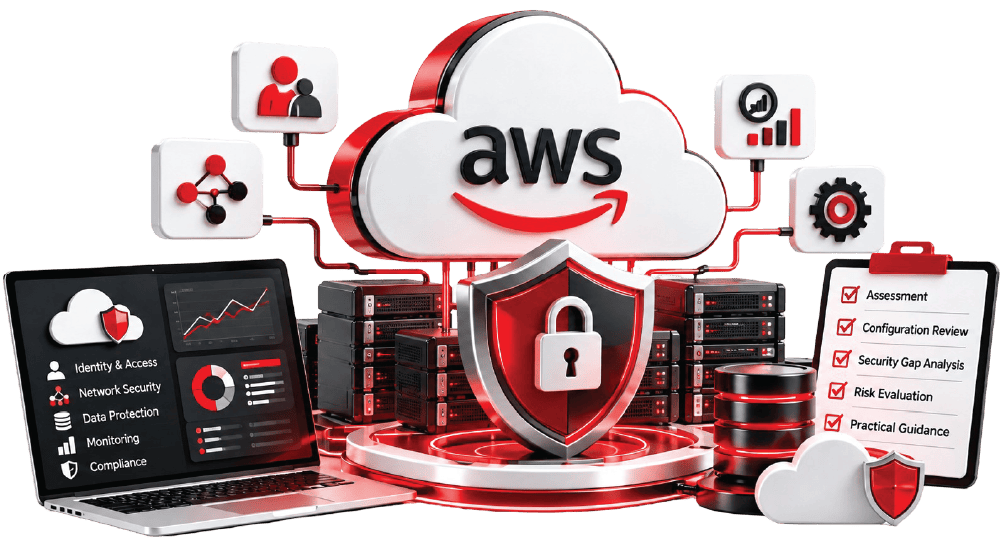
SecureLink helps organizations understand the security posture of their AWS environments through structured assessments, configuration reviews, and identity and access evaluations. We examine the controls relevant to the agreed scope and translate findings into practical recommendations for improving cloud security.
Whether you operate an established AWS environment, are expanding cloud workloads, or need a clearer view of security gaps, our consulting approach connects technical findings with business risk, remediation priorities, and operational ownership.
The assessment scope can cover identity and access management, network exposure, logging and monitoring, data protection, encryption settings, and other relevant AWS security controls.
DISCUSS YOUR AWS SECURITY REQUIREMENTS →SecureLink organizes AWS security consulting around the controls, configurations, and access mechanisms that influence the security of your cloud environment.
Review AWS security controls, relevant configurations, access patterns, and potential exposure to identify weaknesses that require investigation or remediation.
Assess applicable security and compliance requirements against relevant AWS controls, identify potential gaps, and help teams organize remediation actions and supporting evidence.
Examine IAM users, roles, policies, permission assignments, and trust relationships to identify excessive privileges, unnecessary access, and opportunities to strengthen access governance.
Review selected AWS services and configuration settings to identify potential misconfigurations involving network access, encryption, logging, resource exposure, and security monitoring.
Each engagement is scoped around the organization's AWS environment, business requirements, and security objectives. The assessment focuses on relevant controls rather than assuming that every AWS service or security domain requires the same level of review.
Review IAM policies, roles, permissions, trust relationships, and administrative access. Identify opportunities to strengthen least-privilege access and improve accountability across cloud resources.
Evaluate relevant network configurations, security groups, network access controls, and public-facing resources to identify unintended exposure and potential access restrictions that need attention.
Review applicable data protection settings, encryption configurations, and access controls associated with AWS storage and other in-scope services. Identify gaps that may require configuration changes or stronger governance.
Assess relevant logging and monitoring configurations to determine whether security-relevant activity is being recorded and whether existing monitoring arrangements support investigation and response requirements.
Examine selected AWS resource configurations and security controls to identify weaknesses, inconsistent settings, and potential risks across the agreed assessment scope.
Document identified issues, explain their potential impact, and prioritize recommended actions according to risk, operational constraints, and remediation dependencies.
Effective AWS security consulting connects technical assessment with corrective action. SecureLink helps organizations understand identified weaknesses, evaluate remediation options, and establish clear responsibilities for improving their cloud security posture.
Assess in-scope AWS resources, access controls, and security configurations to establish a practical view of existing control coverage and potential weaknesses.
Identify opportunities to reduce excessive permissions, strengthen privileged access, improve role assignments, and align access policies with least-privilege principles.
Recommend changes to relevant AWS security settings, resource permissions, network controls, encryption configurations, and logging arrangements based on assessment findings.
Map relevant requirements to applicable security controls, identify areas requiring attention, and help organize corrective actions and supporting documentation.
A structured assessment process helps ensure that security findings are relevant, documented, and actionable.
Clarify business requirements, AWS account scope, workload sensitivity, security objectives, existing controls, and applicable compliance considerations.
Review agreed AWS configurations, IAM permissions, network exposure, data protection settings, logging, and other relevant security controls.
Document potential misconfigurations, access weaknesses, control gaps, and other findings supported by the assessment evidence.
Organize findings according to risk, potential business impact, exposure, remediation urgency, and operational dependencies.
Develop practical remediation recommendations that address identified issues while considering workload requirements and operational constraints.
Where included in the engagement, review evidence of completed corrective actions and reassess the relevant controls to determine whether the identified issues have been addressed.
A useful AWS security assessment should give technical and business stakeholders a clear understanding of identified issues, their implications, and the next steps required.
A documented summary of the security controls reviewed, the assessment scope, and the weaknesses identified during the engagement.
Observations relating to excessive permissions, access policies, roles, trust relationships, and other identity-related issues within the agreed scope.
A record of relevant configuration weaknesses and potential exposure involving in-scope AWS services, network settings, encryption, and logging.
Where compliance mapping is included, a summary of relevant requirements, associated control gaps, and areas requiring further evidence or corrective action.
A practical sequence of recommended improvements based on risk, business impact, technical dependencies, and implementation priorities.
Documented recommendations covering applicable access controls, configuration changes, monitoring improvements, and other corrective measures.
Where validation is included, a summary of the corrective actions reviewed and the evidence available to confirm whether identified issues have been resolved.
AWS security consulting is useful when an organization needs a clearer understanding of cloud security risks or wants to strengthen existing controls.
Assess current security configurations and access controls to identify potential weaknesses before they develop into more significant operational risks.
Review user, role, and policy assignments when access rights have expanded over time or no longer reflect current responsibilities.
Identify gaps between applicable requirements and existing AWS controls, and organize remediation activities and supporting evidence.
Examine relevant resource settings when changes to infrastructure, applications, or access policies may have introduced security weaknesses.
Evaluate logging and monitoring configurations to understand whether relevant security events are captured and available for investigation.
Review security controls before introducing additional workloads, accounts, integrations, or sensitive data into the AWS environment.
Develop a structured remediation plan when internal reviews, audits, or previous assessments have identified issues that require corrective action.
The right provider should be able to explain security findings clearly, connect them to business risk, and recommend improvements that are practical for the organization's AWS environment.
Look for a structured approach to reviewing AWS configurations, access controls, and relevant security mechanisms, supported by clear assessment scope and documented findings.
The provider should understand IAM policies, roles, trust relationships, privilege boundaries, and least-privilege access principles.
Security recommendations should consider the organization's applicable regulatory, contractual, and internal requirements without assuming that a single set of controls satisfies every obligation.
Findings should identify the affected control or configuration, explain the potential impact, and distinguish confirmed observations from risks that require further investigation.
Recommendations should be specific enough for technical teams to understand the proposed corrective actions and their implementation priorities.
Assessment boundaries, deliverables, responsibilities, remediation ownership, and any validation activities should be agreed before work begins.
SecureLink provides AWS security consulting for organizations in Saudi Arabia seeking a structured approach to cloud risk identification, access governance, security configuration, and compliance-related control improvements.
Review relevant AWS controls and configurations to identify potential weaknesses and establish prioritized security improvement actions.
Evaluate access policies, permissions, and role assignments to support stronger control over who can access cloud resources and what actions they can perform.
Assess relevant AWS settings and resource exposure to identify potential misconfigurations and opportunities to improve protection.
Help organizations map applicable requirements to relevant AWS controls, identify potential gaps, and organize remediation priorities and supporting evidence.
SecureLink focuses on practical security assessment, clear findings, and actionable recommendations that help organizations make informed decisions about their AWS environments.
Assessment activities are aligned with the agreed scope, relevant AWS resources, and the security risks that matter to the organization.
Access reviews focus on identifying unnecessary privileges, reviewing permissions, and recommending improvements aligned with least-privilege principles.
Findings are connected to relevant configurations and controls, helping technical teams understand what requires attention and why.
Where required, security assessments consider applicable compliance obligations and help identify gaps that need further review or remediation.
Recommendations are organized to support practical planning, technical ownership, and a more structured approach to resolving identified issues.
Assessment boundaries, reporting requirements, and any follow-up validation activities are established according to the engagement requirements.
Share your AWS environment details, security objectives, and the controls you want to assess with SecureLink. We can help define a suitable assessment scope, identify relevant review areas, and establish practical priorities for strengthening your AWS security posture.
Practical answers about AWS cloud security assessments, IAM reviews, configuration assessments, and compliance consulting.