AWS Landing Zone Architecture
Define organizational units, account boundaries, shared services and governance responsibilities around your workloads.
SecureLink helps organizations establish an AWS landing zone in Saudi Arabia with a governed multi-account foundation, clear account boundaries and repeatable operational controls. Our AWS Control Tower in Saudi Arabia services align AWS Organizations, identity, logging and governance decisions with business requirements and the way your teams operate.
Whether you are creating a new AWS environment or improving governance across existing accounts, our approach can cover landing zone design, AWS Control Tower implementation, account structure, guardrails, account provisioning and technical handover.
Structure accounts and governance responsibilities.
Establish a governed multi-account AWS foundation.
Apply agreed policies, logging and oversight practices.
Separate workloads, teams and shared services clearly.
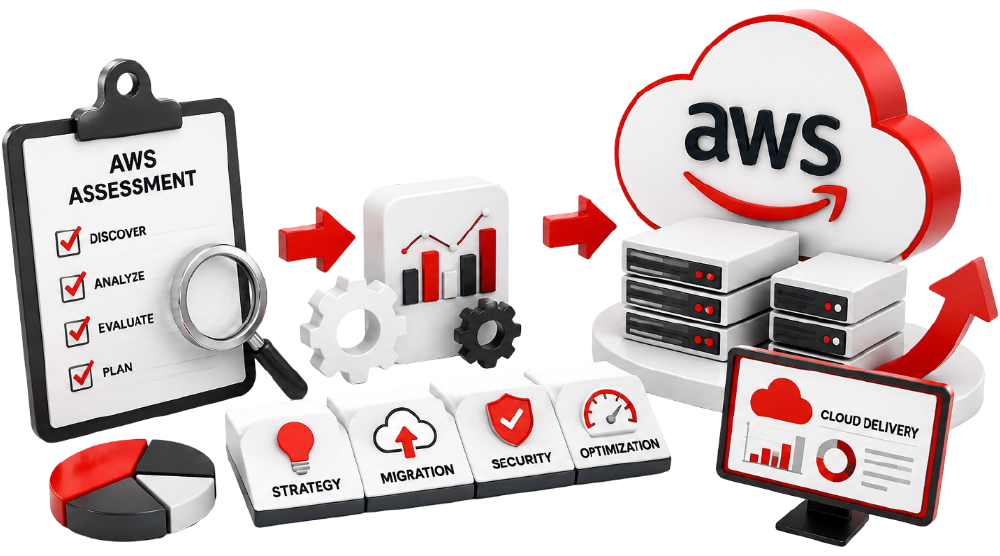
SecureLink helps organizations plan a landing zone that reflects their account structure, operational ownership and security requirements. We review the current environment, identify design dependencies and define an approach for AWS Control Tower and AWS Organizations where they suit the environment.
For organizations adopting an AWS multi-account landing zone in Saudi Arabia, the scope can include organizational units, account provisioning, identity integration, logging, governance guardrails, baseline configuration and a documented handover, with implementation priorities agreed before changes are made.
DISCUSS YOUR LANDING ZONE REQUIREMENTS →We design AWS multi account architecture in KSA around account separation, governance guardrails, operational visibility and repeatable account onboarding across your organization.
Define organizational units, account boundaries, shared services and governance responsibilities around your workloads.
Configure the agreed landing zone capabilities, guardrails and account provisioning workflows where suitable.
Plan organization structure, organizational units, policy requirements and account governance.
Separate production, non-production, security and shared-services workloads with clear ownership and access boundaries.
AWS Control Tower implementation can connect account structure, governance policies, audit visibility and repeatable operations into one clear foundation, according to your requirements.
Define organizational units and account groupings that reflect workload ownership, environments and shared functions.
Define the preventive and detective controls, account policies and oversight processes required for the environment.
Plan centralized log collection and monitoring practices to support investigation, visibility and operational oversight.
Set out account onboarding workflows, operating responsibilities, documentation and the transition to internal cloud operations.
Successful landing zone delivery connects account architecture, access, governance and day-to-day operating ownership.
Define the target account structure, organizational units, shared services and governance boundaries.
Plan implementation of landing zone configuration, governance guardrails and account provisioning capabilities in scope.
Align AWS Organizations policies, identity, logging and account responsibilities with your operating model.
A staged implementation approach makes dependencies, control decisions, ownership and acceptance criteria clear before changes are introduced.
Review AWS accounts, business objectives, workloads, identity, dependencies and operational requirements.
Identify readiness gaps, account dependencies, governance needs and prerequisites for adopting the target model.
Define organizational units, account boundaries, Control Tower approach, policies, logging and responsibilities.
Configure the agreed foundation and governance components in a controlled sequence with suitable validation.
Check agreed controls and workflows, document key decisions and hand over operating guidance to your team.
Deliverables are agreed in advance so stakeholders know what will be designed, configured, validated and transferred to the cloud operations team.
Record the existing AWS accounts, identity setup, workload dependencies, policies and operational constraints affecting the landing zone design.
Document account structure, organizational units, shared services, governance boundaries and the key architecture decisions.
Set out the implementation phases, prerequisites, account onboarding sequence, dependencies and acceptance criteria.
Document the agreed identity, access, logging, monitoring and governance baseline; validate detailed compliance obligations separately.
Record the planned configuration activities, control validation, account provisioning checks, ownership and handover actions.
Provide operating guidance, account onboarding notes, responsibilities and recommendations for extending the landing zone over time.
A landing zone is especially useful when account growth, governance responsibilities or security expectations make an ad hoc account-by-account approach difficult to manage.
Establish account structure and governance foundations before teams begin deploying production workloads and shared services.
Review current account ownership, access practices, logging and policies before adopting a consistent multi-account governance model.
Check prerequisites and define the Control Tower rollout, landing zone configuration, guardrails and onboarding approach.
Use account boundaries to distinguish environments, teams and shared functions where separation supports operational and access requirements.
Define repeatable provisioning workflows so newly created accounts can follow the agreed configuration and governance baseline.
Create clearer policy ownership, central visibility and operational processes as cloud use expands across the organization.
A strong implementation partner should connect architecture, AWS Organizations, Control Tower configuration and operational handover rather than treating each control as an isolated task.
Can the team design account boundaries, organizational units and shared services around your operating needs?
Can the team plan prerequisites, guardrails, provisioning workflows and a controlled implementation?
Are access, logging, policy ownership and operational guardrails considered from the beginning?
Are responsibilities, configuration records, operating guidance and next steps clear after implementation?
SecureLink helps organizations across Saudi Arabia plan landing zone architecture and AWS Control Tower implementation around their existing accounts, security expectations, business priorities and operating model.
Plan a governed landing zone and repeatable account provisioning approach where Control Tower fits the environment.
Set clear account boundaries, policy ownership, access responsibilities and logging practices.
Assess account readiness and plan a staged path for bringing eligible accounts into the agreed governance model.
SecureLink brings landing zone architecture, Control Tower planning, AWS Organizations design and governance considerations together with clearly defined implementation scope and handover.
Account structure and governance decisions are aligned with business needs, workload boundaries and operational responsibilities.
Identity, access, logging and policy requirements are considered as part of the agreed foundation.
Landing zone design, Control Tower configuration, account governance and validation can be planned as coordinated workstreams.
Documentation, ownership and operating guidance help internal teams understand the implemented foundation and next steps.
Share your AWS account structure, governance priorities and technical requirements with SecureLink. We can help define a practical scope for AWS Control Tower implementation and multi-account architecture in Saudi Arabia.
Answers to common questions about AWS landing zone design, AWS Control Tower, AWS Organizations and multi-account architecture in Saudi Arabia.