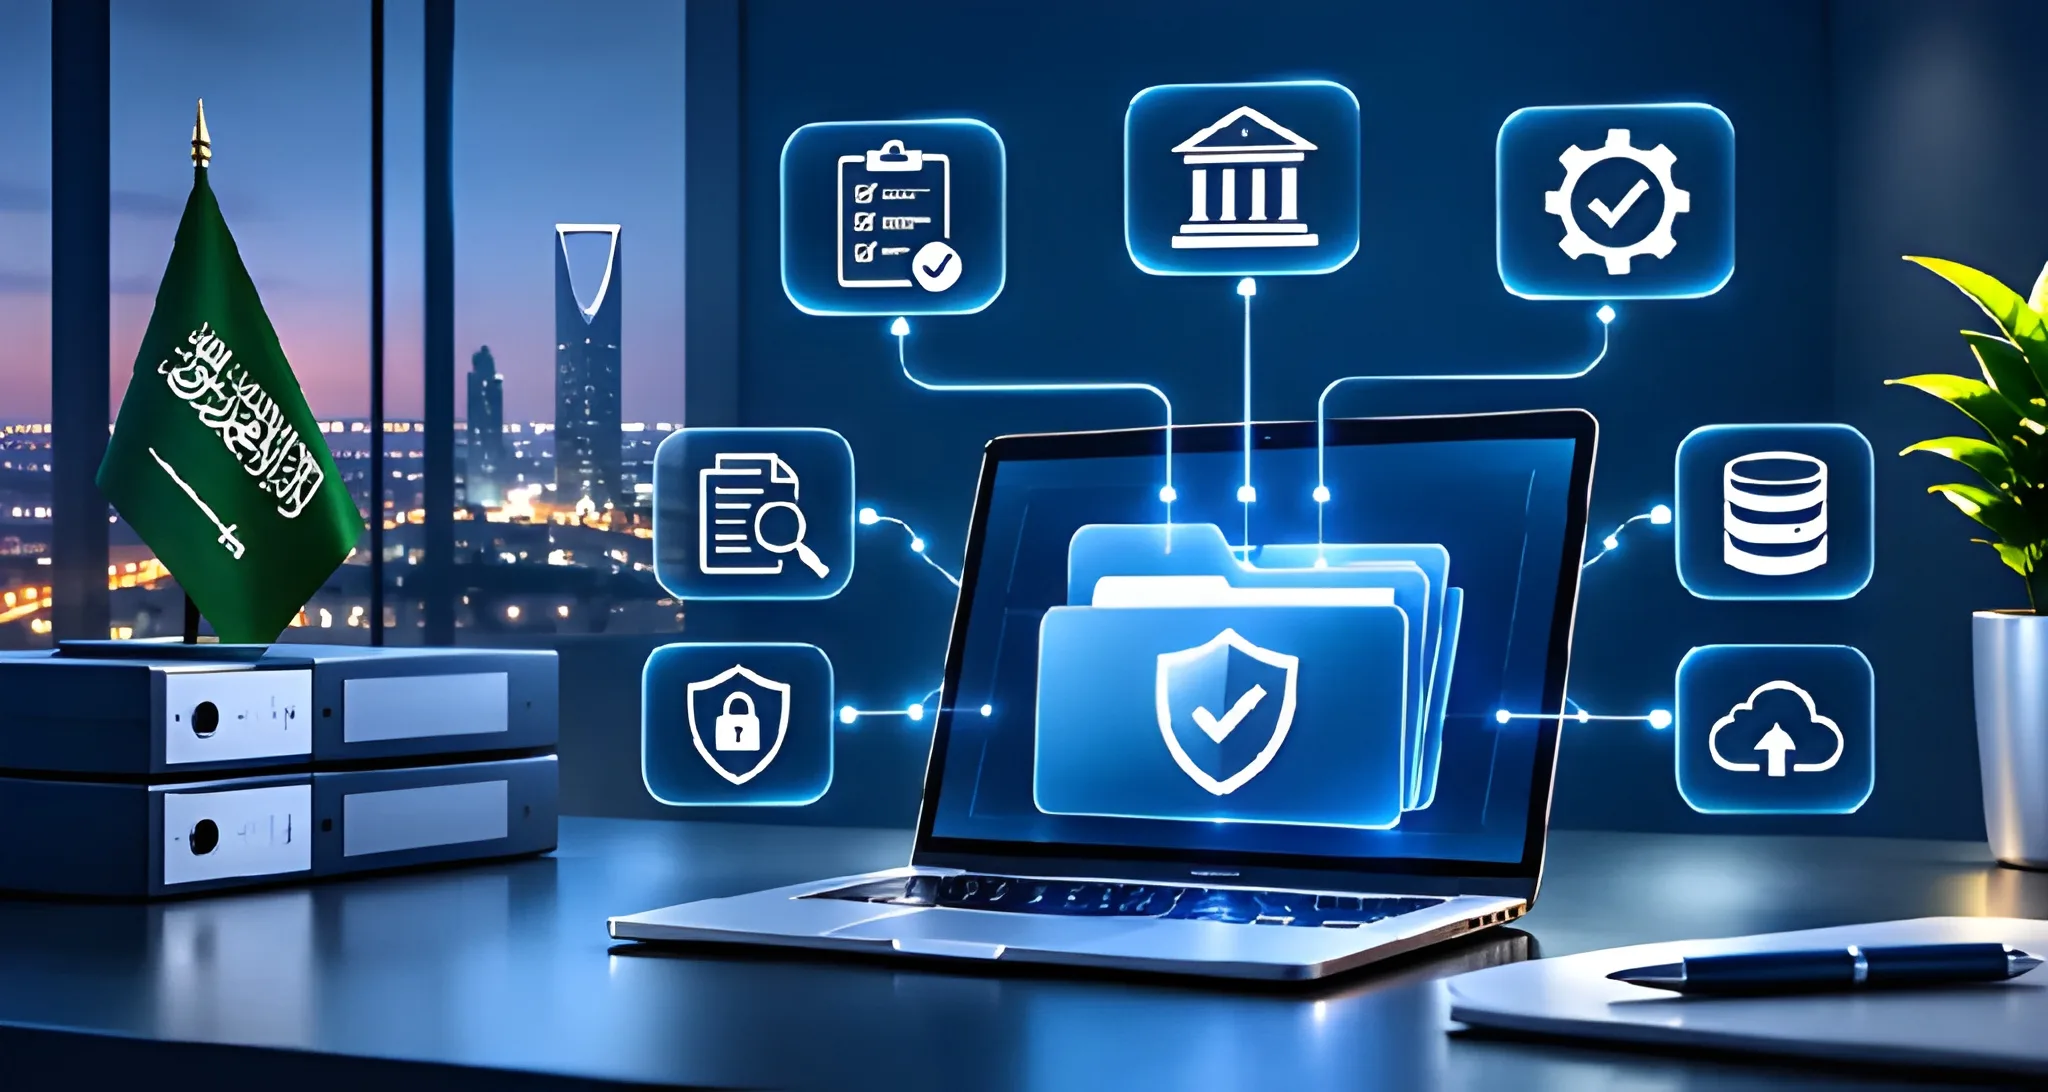
Managing governance, risk, and compliance documentation becomes increasingly challenging as Saudi businesses expand their operations and face multiple regulatory requirements. A Centralized GRC Evidence Repository offers a controlled method of managing significant records, keeping proper documentation, and accessing compliance information when required. It also assists organisations in cutting the administrative workloads and enhance communication among the departments.
As the requirements of cybersecurity regulations, audit expectations and data protection changes, companies require trusted evidence management practices. Effective processes and professional GRC services in Saudi Arabia can assist organisations to enhance accountability, regulatory preparedness and ensure ongoing compliance. SecureLink assists companies to create a form of structured governance and compliance practices.
What Is a Centralized GRC Evidence Repository?
A Centralized GRC Evidence Repository is a safe online place where organisations store, manage and access governance, risk and compliance records. It consolidates vital records rather than having them in different systems, emails, and departmental folders, which are not interconnected.
Policies, risk assessment, audit report, regulatory evidence and corrective action records are managed in this repository by businesses. It enhances document visibility, promotes accountability, eases auditing, and assists employees with authorisation to easily access trustworthy information.
Why Do Saudi Businesses Need a Centralized GRC Evidence Repository?
Saudi companies deal with the regulatory frameworks that entail requirements by government bodies like NCA, SAMA, CST, and other pertinent regulators. Scattered documentation makes it hard to verify compliance and in assessments, such documentation may lead to the loss of important evidence.
A centralised system enhances regulatory preparedness, enhances internal coordination and facilitates quicker preparation of audit. It also aids organisations to show accountability, keep a track of compliance activities, detect documentation gaps, and have a uniform evidence of all business operations.
What Documents and Evidence Should a GRC Repository Include?
Governance Documentation
Governance documentation comprises of approved policies, organisational structures, committee meeting minutes, delegation records and management approvals. The documents create a sense of accountability, leadership control, delineate responsibilities, and show evidence of steadfast governance practices.
Risk Management Documentation
Risk management documents encompass risk registers, assessment report, treatment plan, mitigation plan as well as business impact analysis. Keeping these documents assists organisations to track exposures, test effectiveness of the controls, trace ownership and show the continuous risk management efforts.
Compliance Documentation
Compliance documentation includes regulatory compliance, control mappings, compliance testing, internal procedures and supporting evidences. The organisations are advised to keep the records updated showing how the applicable obligations are met, monitored, reviewed, and integrated into the normal business processes.
Cybersecurity and IT Evidence
Examples of cybersecurity evidence are vulnerability assessments reports, penetration tests, access reviews, security configurations, incident documentation, and logs. These documents show the implementation of security control and assist in regulatory evaluations and technical reviews and improve cybersecurity programs.
Audit and Corrective Action Records
Audit records consist of in-house audit reports, external evaluation reports, evidence request forms, remediation strategies and termination approvals. The benefits of keeping such records include assisting organisations in tracking outstanding issues, delegation, verifying improvement and accountability in the process of audit cycles.
How to Build a Centralized GRC Evidence Repository: Step-by-Step Guide
Step 1 – Identify Applicable Regulatory and Compliance Requirements
Determine applicable regulatory requirements prior to gathering evidence based on NCA, SAMA, CST, PDPL and industry requirements. Applicable controls, reporting requirements, evidence requirements, and responsible departments to come up with clear repository requirements.
Step 2 – Assess Existing Documentation and Evidence
Conduct an audit of policies, risk register, audit reports, compliance records, and documents of cybersecurity, across departments. Determine the evidence that is missing, old versions, overlaps, inconsistent formats and ownership, prior to starting repository development.
Step 3 – Define a Standardized Evidence Structure
Create a Centralized GRC Evidence Repository model based on regulatory domains, category of controls, departments and type of documents. Use uniform naming, folder structures, metadata categories and classification criteria to effectively access information.
Step 4 – Assign Evidence Owners and Responsibilities
Establish a clear ownership of departments, control owners and document administrators who are to maintain certain evidence. Establish deadlines, approval authorities, reviewing and escalation steps to enhance accountability and avoid gaps in documentation.
Step 5 – Select the Right Repository Platform
Select a Centralized GRC Evidence Repository service that will facilitate secure storage, classification of documents, automated workflow, access control, and audit trails. Consider scalability, integration, usability and compatibility with the current organisational systems.
Step 6 – Implement Access Controls and Version Management
Create role permissions to allow employees to have access to documentation that they are authorised to. Allow tracking of versions and approval records, encryption and secure backups to ensure that sensitive records are not violated and documents are not manipulated.
Step 7 – Establish Review and Update Procedures
Establish routine policy review, compliance documentation, risk assessment and audit documentation. Establish due dates, inform the duty holders, check regulatory amendments and substitute old records with new ones by having controlled approval procedures.
Step 8 – Monitor Repository Effectiveness
Track the performance of the repository by documentation completeness, evidence retrieval time, outstanding reviews and corrective actions. Periodically carry out evaluations to determine areas of weakness, enhance processes, and ensure a consistent set of compliance records by department.
Common Challenges in Managing a Centralized GRC Evidence Repository
1. Scattered Documentation Across Departments
Various departments tend to have a different folder, spreadsheets and document management systems. This discontinuity results in duplicate records, inconsistencies, and retrieval problems, and coordinating compliance management and audit preparation becomes more difficult.
2. Outdated or Incomplete Evidence
Employees can also ignore the planned updates, and leave policies, assessment reports, and compliance records obsolete. Unfinished documentation undermines audit preparedness, poses challenges in verification and makes it harder to prove that controls are well implemented.
3. Unclear Document Ownership
In the absence of a defined allocation of responsibilities, the employees might think that another department has some important records. This poses accountability loopholes, slows the pace of evidence gathering and elevates the chances of oversight when carrying out regulatory evaluations.
4. Inconsistent Naming and Classification
Various departments can adopt a variety of naming schemes, folder hierarchy and document type to store evidence. In the absence of standardisation, workers find it difficult to find pertinent records, version compare and find documentation related to certain regulatory controls.
5. Insufficient Security and Access Management
Weak permission settings may make confidential compliance documents to fall into the hands of unauthorised staff. Poor access control, poor backup systems and absence of version controls also pose risks of information disclosure, accidental changes and loss of documents.
Best Practices for Maintaining a GRC Evidence Repository
1. Maintain Consistent Documentation Standards
Define organisation-wide document naming, formatting, classification and storage guidelines. Stable standards make the employees find pertinent evidence fast, minimize duplication, and ensure good documentation across various departments and compliance exercises.
2. Schedule Regular Evidence Reviews
Establish a policy of recurring policy review schedules, control records, risk assessment and supporting documents. Allot accountable owners and keep track of deadlines so that information is always accurate, current, complete and in compliance with this on changing regulatory needs.
3. Strengthen Document Security
Protect sensitive records by implementing role-based permissions, multifactor authentication, encryption and activity monitoring. Periodically check access of users and delete unneeded permissions to ensure confidentiality as well as limit unauthorised access to documents.
4. Automate Evidence Collection and Notifications
Automate workflow to gather supporting documents, inform responsible employees and monitor approvals. Automation helps cut down on the repetitive administrative tasks, enhances the consistency of submissions, and assists compliance teams to detect overdue evidence early.
5. Maintain Reliable Backup and Recovery Procedures
Put in place secure backup schedules and often test recovery procedures to safeguard valuable compliance documentation. Ensure relevant retention and recovery plans and policies to ensure continuity of the business and avoid irreversible loss of evidence.
How Professional GRC Services Help Saudi Businesses Improve Evidence Management
1. Regulatory Requirement Identification
Professional consultants assist organisations to determine the relevant Saudi regulatory requirements and address the obligations into realistic evidence expectations. This methodology sets more defined documentation priorities, enhances control mapping and eliminates doubt in preparing compliance.
2. Repository Design and Implementation
Skilled GRC practitioners assist companies to develop ordered repository frameworks that are in line with organisational activities and regulatory demands. They define the categories of documents, naming system, ownership and workflow used to assist in the management of evidence in a consistent manner.
3. Compliance Gap Assessment
GRC professionals compare the existing documentation with the relevant regulatory controls and discover missing or inadequate evidences. Their evaluations assist organisations in prioritising corrective actions, enhancing documentation standards, and enhancing the overall compliance preparedness.
4. Governance and Risk Management Improvements
Professional support aids organisations to enhance the management of policies, recording of risks, control ownership and reporting. These enhancements enhance the interdepartmental coordination and establish better records of the management decisions and risk treatment endeavors.
5. Continuous Monitoring and Compliance Support
Continued GRC assists organisations in document review, regulatory changes and in filling emerging gaps of evidence. Frequent evaluations and recommendations to improve keep the repositories effective as well as help sustain sustainable governance and compliance management practices.
Conclusion
Developing a Centralized GRC Evidence Repository is a way to enable Saudi companies to store key governance, risk, cybersecurity and compliance documentation in a well-organised space. Organisations can enhance audit readiness and ensure a better regulatory supervision through setting standardised documentation, having clear ownership, security measures, and regular reviews. A properly managed repository also minimizes the documentation gaps, easiness in retrieving evidence and facilitates improved coordination among the departments.
Nevertheless, to ensure efficient evidence management, one needs to pay constant attention, have the right technology and be aware of regulations. The documentation practices of businesses should be reviewed regularly, internal controls enhanced and new compliance requirements met. These practices promote sustainable governance, operational transparency and resilience of organisations over the long run.